

Google Authenticator
by Google LLC
3.8
- Safety
- 100% Safe
- Category
- Tools
- Ratings
- 3.8
- Price
- Free
- Download
- 100.00M
This app is secure, reliable, free to install, and offers fast downloads without any risks or malware.
Screenshots
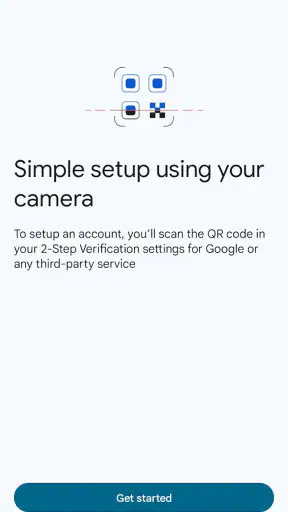
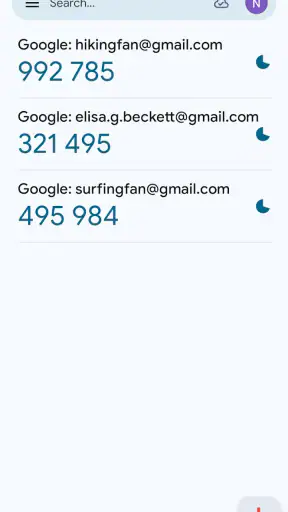
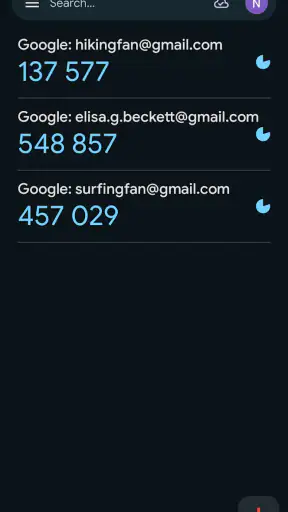
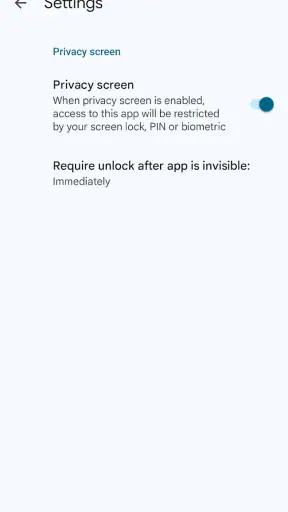
 Analysis by Getfullapps
When I first set up Google Authenticator, the appeal was immediate: it gave me a quick way to add an extra checkpoint to account sign-ins without turning security into a daily project. The app is free, belongs to the Tools category, and comes from Google LLC. Its job is narrow, but that is part of its strength. It is not trying to become a password manager, a messaging service, or a general security dashboard. It is a focused companion for two-step verification.
That focus also makes it easy to misunderstand. Installing it alone does not protect every account I own. I still have to enable two-step verification inside each supported account and connect that account to the authenticator. Once configured, the app generates temporary verification codes that I enter when a service asks for the second step. The result is simple from the user’s side, although the first setup can feel less obvious than the polished store summary suggests.
My overall view is that Google Authenticator earns lasting space when I treat it as a small security habit rather than an app I actively use every day. It rarely demands attention, and that is exactly why it can remain useful for months. The trade-off is that it becomes important during stressful moments: signing in on a new phone, recovering access, or dealing with a service that suddenly requests verification. A little preparation matters more here than frequent interaction.
Why the first week feels so convincing
During the first week, the main satisfaction comes from seeing how little effort is needed after setup. I open an account’s security settings, choose an authenticator-based verification method, scan the displayed setup code or enter the provided key, and then confirm a generated code. After that, the account appears as an entry in the app, ready for future sign-ins. The process is repetitive, but it is understandable once the first account is connected.
The interface is intentionally restrained. I can recognize an account from its label, read the current code, and wait for the countdown to refresh. There is no distracting feed or complicated security terminology competing for attention. For someone who wants a straightforward two-step verification app, that simplicity is more valuable than a long list of secondary tools.
One practical detail I learned quickly is that account labels deserve care. If several entries use similar names, finding the right code during a login becomes slower and more error-prone. I prefer labels that include the service and, where necessary, the account identity in a recognizable way. This is a small organizational choice, but it becomes important once the list grows beyond a handful of entries.
Another useful habit is to add accounts while I am already signed in and calm, not while I am locked out and rushing. The setup secret or QR code belongs to the account’s security process, so I treat it as something to handle deliberately. I also keep the recovery options offered by the service available before changing security settings. The authenticator can generate the code, but it cannot replace every recovery method a service may require.
Articles to Explore Next

Uber Eats Makes Dinner Easier to Manage, but the Fees Add Up

Google Photos Turns a Camera Roll Into a Library You Can Find Your Way Through

Canva on Mobile: Adopt It for Quick Visuals, Test It for Demanding Work

Google Drive Keeps Work Moving Until It Doesn’t

Switching to Weather - By Xiaomi Means Relearning Your Forecast Routine

Ludo King and the Social Life of a Lucky Six
The first-week experience is especially good for people who have avoided authenticator apps because they assumed they would be complicated. Google Authenticator does not require me to understand cryptography to use it. I only need to follow the account’s instructions, add the entry correctly, and enter the changing code when prompted. That low learning curve helps turn a security recommendation into something I will actually complete.
Still, the first setup is not universally smooth. Some services use different wording for their security menus, and the authenticator is not always the only step involved. A user may need to confirm a password, approve an email, save recovery codes, or complete another verification method. Those parts happen outside the app, so I would not blame the authenticator for every confusing setup screen, but the overall experience can still feel fragmented.
The everyday scenario that explains its value
Imagine signing into an important account from a borrowed computer while traveling. The password may be correct, yet the service asks for a second code. I open the authenticator on my phone, locate the matching entry, read the current code, and type it into the sign-in screen. No text message has to arrive at that moment, and I do not have to wait for a network-delivered message before continuing. That is the kind of small, practical moment in which the app proves its worth.
This workflow also shows why the phone itself matters. If I leave it behind, lose access to it, or replace it without planning, the convenience can quickly become an obstacle. I therefore see the app as a reliable tool only when it is part of a wider account-recovery plan. The code is useful, but access to the device and knowledge of the correct account entry are equally important.
What remains useful after the novelty fades
After the first month, the app becomes almost invisible. I do not open it to browse or explore; I open it when a particular account requests a code. That may sound like weak engagement, but security tools should not be judged by entertainment-style usage. Its recurring value comes from being available at the exact point where a password alone is not enough.
The strongest long-term case is for accounts that matter: email, work services, financial tools, cloud storage, and any account that could expose other logins. I would not automatically add every minor service. Each additional entry creates a little more maintenance and another possibility of confusion later. A selective approach keeps the list useful instead of turning it into an unstructured collection of codes.
Compared with receiving codes by text message, an authenticator-based method can be more convenient when mobile delivery is delayed or unavailable. It also avoids depending on a message arriving at the precise moment I am trying to sign in. On the other hand, text messages can feel easier for people who rarely change phones and do not want to manage an additional app. The better choice depends on the account’s options and the user’s ability to maintain access.
Compared with a password manager that includes one-time-code support, Google Authenticator is more focused but less comprehensive. A password manager can place passwords and verification codes in one workflow, which may be better for someone who already relies on that system. The separate authenticator approach creates a useful boundary between the password and the second factor, but it also means I may move between apps during sign-in.
Hardware security keys are another alternative, particularly for people who want a physical sign-in device and are willing to carry it. They can offer a different kind of protection and a different recovery experience. I would choose a hardware key for a high-risk account or a carefully managed professional setup when that method is supported. I would choose Google Authenticator when I want a free, familiar, phone-based option that I can deploy quickly.
Its broad reach helps explain why it remains easy to recommend. The app has passed one hundred million installs, carries an average rating of 3.8 from around 668 thousand ratings, and is marked for Everyone. Those figures do not tell me whether it fits my personal workflow, but they do show that it is not an obscure specialist tool. It has become a recognizable entry point for people who are beginning to take account security seriously.
Small workflows that make a big difference
My first long-term tip is to review the entries whenever I close an old account. Leaving unused entries in place does not make the app more secure, and it makes the list harder to scan during a real login. I remove obsolete items only after I am certain the associated account is closed or has moved to another verification method.
My second tip is to test access before changing phones. I do not wait until the old device is being wiped or traded in. I sign into the relevant accounts while I still have a working path, check the recovery choices, and follow the service’s instructions for transferring or re-enrolling the authenticator where available. The exact process belongs to each account, so preparation is more dependable than assuming every service behaves the same way.
A third insight is that the countdown is not something I need to fight. If a code is close to expiring, I wait for the next one rather than repeatedly entering a number that may become invalid. When signing in on a computer, I keep the phone and login screen visible together and type carefully. This sounds obvious, but it reduces failed attempts when several accounts have similar labels or when the code changes mid-entry.
I also avoid treating a screenshot of a setup code as a permanent backup. Keeping sensitive setup material casually in a photo library can create a different security problem. I prefer to follow the account’s own recovery guidance and store recovery information deliberately. The authenticator is strongest when its setup and recovery details receive the same care as the password.
Maintenance is light, but the consequences are serious
Google Authenticator asks little from me during normal use. I do not need to open it on a schedule, tune complicated settings, or maintain a daily routine. Its maintenance burden is mainly organizational: keeping entries understandable, keeping the phone accessible, and planning for device changes. That is a favorable exchange for a tool that protects important sign-ins.
The burden becomes more noticeable when I add many accounts. A long list can make a simple code lookup feel like searching through a drawer of unlabeled keys. I solve that by using clear account names and removing entries I no longer need. I also avoid adding duplicate entries unless I understand why a service created them. Duplicate-looking records can lead me to copy a valid code from the wrong account and waste time troubleshooting.
Phone replacement is the maintenance event I take most seriously. A new device can be exciting, but it is also the moment when an authenticator requires planning. Before retiring the old phone, I check which accounts depend on it and work through their available transfer or recovery process. I would never assume that installing the app on the new device automatically recreates every account entry. That assumption could leave me facing several locked sign-ins at once.
This is also where the app may not be the right choice for everyone. If I manage many accounts for a team, need centralized administration, or require a carefully documented recovery process, a business-oriented identity system or hardware-based approach may be more suitable. Google Authenticator is designed for personal, direct use. Its simplicity is a benefit for one person, but it does not replace organizational account management.
The app’s free price removes one common barrier, and its age rating of Everyone makes it approachable for a wide audience. It was released on March 21, 2012, which gives it a long presence in the mobile security conversation. I value that familiarity, although longevity alone does not remove the need to think about backup and recovery. A mature tool can still create problems if I use it casually.
Where fatigue starts to appear
The main source of fatigue is not opening the app; it is the interruption during sign-in. I may be trying to approve a purchase, join a meeting, or access a file, and the second step forces me to stop, unlock the phone, find the correct entry, read the code, and return to the original screen. That friction is intentional, but it is still friction. Over time, users may be tempted to disable two-step verification if the process feels repetitive.
Similar account names create another kind of tiredness. The app can show the needed code quickly, but it cannot decide which of several nearly identical entries I intended. Clear naming at setup is therefore more important than it seems. I also find that switching between a phone and another device is easier than trying to remember a code or copy it under pressure.
There is a psychological cost as well. Security tools make me think about failure scenarios: a lost phone, a forgotten recovery method, or an account that suddenly demands verification. That awareness is healthy, but it can make the app feel like another responsibility. I reduce that feeling by handling recovery planning in one sitting instead of worrying about it every time I open the app.
Some people should skip this option in favor of a different method. If they regularly lose access to their phone, share devices, or dislike maintaining account-specific security settings, text-based verification may feel more manageable, though it has its own weaknesses. If they already use a trusted password manager with integrated code generation, adding a separate app may create unnecessary duplication. If an account supports a security key and the user wants stronger physical control, that route may be preferable.
There is also a fairness issue in recommending any authenticator without explaining the recovery responsibility. Telling someone to “just use an authenticator” is incomplete advice. I would recommend it together with a reminder to identify recovery codes, alternate sign-in methods, and the steps needed before a phone is replaced. That guidance is not an optional extra; it is what turns a convenient setup into a sustainable one.
Does it deserve permanent space on my phone?
For me, Google Authenticator passes the long-term test because its value returns whenever an important account needs a second proof of identity. It does not rely on novelty, frequent updates to my routine, or a large feature set. Once I have configured the accounts I care about, the app settles into the background and does its job with minimal attention.
I recommend it to anyone who wants a free and direct way to use authenticator codes for personal accounts, especially if they are comfortable planning ahead for a phone change. It is also a sensible starting point for someone moving beyond passwords for the first time. The setup is approachable, the purpose is clear, and the app does not bury the core task under unrelated features.
I would be more cautious about recommending it to someone who expects automatic recovery, a built-in password vault, or a complete account-security command center. It is not a magic shield, and it cannot compensate for weak passwords, careless handling of setup secrets, or missing recovery planning. Users with complex professional needs may be better served by managed identity tools, hardware keys, or a password manager that fits their existing workflow.
My final judgment is favorable, with one condition: use it deliberately. Add only the accounts that matter, label them clearly, keep recovery options in order, and prepare before changing phones. With those habits, Google Authenticator becomes the kind of app I almost forget is installed until the exact moment I need it. That quiet, recurring usefulness is enough to earn its place.
Pros
- Easy to set up with multiple accounts
- Works offline without internet access
- Simple and clean user interface
- Supports time-based one-time passwords
- Enhances security with two-step verification
Cons
- No backup option for lost devices
- No biometric authentication support
- Limited customization features
- Requires manual transfer to new devices
- No desktop version available
FAQs for Google Authenticator
What is Google Authenticator used for?
Google Authenticator is used for two-factor authentication (2FA), which adds an extra layer of security to your online accounts. By generating time-based, one-time passcodes, it helps ensure that even if someone knows your password, they won’t be able to access your account without the code from the app.
How do I set up Google Authenticator on my device?
To set up Google Authenticator, download the app from the Google Play Store or Apple App Store. Open the app, then scan the QR code provided by the website you’re securing. This will link your account to the app, allowing it to generate codes that you’ll use for logging in.
Can I use Google Authenticator on multiple devices?
Google Authenticator does not natively support syncing across multiple devices. To use it on another device, you need to manually set it up again by scanning the QR codes for each account. It’s important to keep backup codes safe in case you lose access to your original device.
What happens if I lose my phone with Google Authenticator installed?
If you lose your phone, you’ll need to use backup codes provided during the initial setup of each account. These codes allow you to regain access. Alternatively, some services offer alternative verification methods, like SMS. Always ensure you have a backup method ready.
Is Google Authenticator free to use and are there any ads?
Yes, Google Authenticator is completely free to use and does not contain any ads. It’s designed to be a simple, efficient tool for enhancing your digital security without any additional costs or distractions from advertisements.
Read About Google Authenticator in Your Language

Google Authenticator
This site provides independent information about third-party apps and is not affiliated with, or the owner, developer, or distributor of, any app featured here. App names, logos, and trademarks belong to their respective owners. Developer details are provided for reference; please contact the developer directly via accounts-support@google.com, visit https://support.google.com/accounts/bin/answer.py?hl=en&answer=1066447, or review their http://www.google.com/policies/privacy.










